CastleRAT Historical Bot Infection Special Report (Stolen Credentials)
November 13, 2026
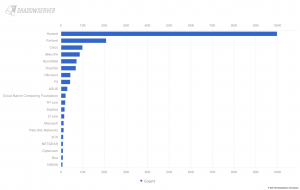
On Thursday 12th November 2026, international law enforcement partners announced "Season 4" of the ongoing Operation Endgame initiative, a public/private partnership with the goal of disrupting major cyber crime enablers globally. This latest action targeted the Gootloader, CastleRAT, and StealC cybercrime-as-a-service families. Law enforcement seized 235 servers and 257 domain, and 6.4 million compromised credentials were acquired. Shadowserver is sharing initial elements of the CastleRAT infostealer data in another one-off Special Report, to allow victims to be notified and compromised credentials triaged and remediated by system defenders. A short, high level analysis of the stolen credentials is also provided.